 Orvus
The journal
Can I use ChatGPT for customer service? A practical, compliance-first guide
AI chatbot for customer service explained, including legal checks, lifecycle steps and measurement to deploy safely and sustain ROI.
What an AI chatbot for customer service actually is , definition and current context
How generative chatbots differ from rule-based bots
An AI chatbot for customer service uses generative models to produce conversational responses rather than relying only on fixed decision trees or scripted replies. Generative systems can rewrite answers, summarize prior chat history and suggest next steps, while rule-based bots follow explicit if then logic and fall back more often to human agents.
In practice that means an AI chatbot can handle the wording and surface variation of common questions and perform agent assist tasks such as drafting replies or summarizing a ticket for a human responder. Teams use these capabilities to reduce repetitive agent work and improve response speed without replacing escalation paths.
Where ChatGPT-style systems are commonly used in support workflows
Common roles for these systems include automated deflection, agent assist and triage, each with a specific operational boundary. Deflection aims to resolve routine queries without human help, agent assist improves live or asynchronous agent productivity, and triage collects structured details before handoff to a specialist.
Market research shows customer service is a leading early use case for generative AI because the workload maps well to repeated conversational tasks and measurable efficiency gains, such as reduced handle time and increased agent throughput McKinsey report.
Service platforms also publish trends indicating similar adoption patterns and benefits in early deployments, making support a common first production target for teams testing generative assistants Zendesk trends.
Can you legally use ChatGPT in customer service? Key regulatory and privacy checks
Transparency and obligation under the EU AI Act
Before deploying an AI chatbot in markets covered by the EU Artificial Intelligence Act, teams must plan for transparency obligations that require users to be informed they are interacting with an AI system and may impose additional controls depending on risk classification EU Artificial Intelligence Act.
These phased obligations mean product and compliance teams should map anticipated enforcement timelines into the deployment plan so that transparency and documentation are ready when enforcement milestones apply.
Data protection controls: DPIAs, lawful basis, retention and minimization
A practical privacy start point is to perform a data protection impact assessment that documents the types of personal data processed, the lawful basis for processing and the planned retention and deletion rules in line with local law.
Regulators advise combining data protection by design and by default with human oversight and clearly documented processing purposes to reduce legal risk and preserve user trust.
quick internal DPIA and privacy control checklist for support bots
Apply data minimization when routing queries to a model, and avoid sending unnecessary identifiers to the API unless required for context or verification. Keep configuration and contract records showing which fields are redacted or hashed before leaving your systems.
Vendor API policies and configuration (OpenAI API data usage)
Vendor policy reviews should confirm whether API inputs and outputs are used to train provider models by default and what contractual controls exist for data retention and deletion. For example, documentation from one major provider indicates that API inputs and outputs are not used to train models by default while leaving retention controls and safeguards to the client organization OpenAI API data usage policies.
Verify vendor terms and implement technical measures such as request filtering, selective logging and private deployments if you need stricter isolation or audit trails than the provider offers by default.
A practical lifecycle framework to deploy a safe, measurable AI chatbot
Plan: risk identification and goal-setting
Start by naming the use cases and the risks for each, for example privacy exposure during billing queries or safety risk in refund decisions. Assign a risk owner and record acceptable risk thresholds and recovery steps before any code is released.
Define measurable goals up front, such as percentage of cases to be handled automatically and target containment or deflection metrics, and tie those goals to user experience and compliance milestones.
Build: design, data controls, and testing
Design controls include prompt standards, scoped context windows, and explicit instructions to avoid giving legal or medical advice. Keep prompts version controlled and document why particular system and user messages exist.
Implement access controls so only authorized services can call the model, and use field-level redaction for sensitive identifiers. Stage environments must mirror production privacy settings so that tests reveal realistic data flows.
Before going live, run staged tests that cover normal flows and adversarial scenarios. Acceptance criteria should include accuracy thresholds, a low rate of unsafe outputs and smooth escalation to humans when confidence is low.
Can my support team use ChatGPT-style models in production without breaching privacy or safety rules?
Yes, but only with clear governance, data protection impact assessment, vendor contract checks and continuous monitoring; consult legal counsel for jurisdiction-specific obligations.
Operate: monitoring, red teaming, and continuous evaluation
Once live, monitor for hallucinations, safety regressions and privacy incidents through sampling, automated checks and user feedback. The NIST Generative AI Profile recommends lifecycle practices such as red teaming and continuous evaluation to detect emergent risks NIST Generative AI Profile.
Maintain a playbook for incidents that specifies who isolates the system, how to rotate keys, and when to notify users or regulators. Regularly update prompts and guardrails based on incidents and measured error patterns.
How to measure success and sustain ROI for an AI chatbot in support
Core metrics to track and why they matter, AI chatbot for customer service
Containment or deflection rate shows how many interactions the bot resolves without human handoff and directly affects cost savings and agent load. Measure containment alongside customer satisfaction to make sure automated resolution is acceptable to customers.
Below we list complementary metrics that together indicate safe, productive performance
- First-contact resolution measures whether a case is resolved at first interaction
- Average handle time captures time spent per interaction when a human is involved
- CSAT captures user-reported satisfaction after bot or agent interactions
- Escalation rate tracks how often conversations require human intervention
- Safety and accuracy error rates measure hallucinations and policy violations
Industry experience suggests ROI is commonly realized through a mix of automated deflection and agent assist, with gains only sustained if teams measure and act on these key metrics McKinsey report.
Run controlled pilots and A/B tests that compare bot assisted flows to human-only baselines, and use predefined escalation triggers to avoid exposing users to risky automated decisions. Use experiment results to decide whether to expand, tune or pause a capability.
Designing experiments and governance for continuous improvement
Design experiments with clear success criteria and statistical rigor, track leading indicators such as early containment lift, and tie experiments to operating budgets and staffing changes so wins translate to durable savings.
Set a reporting cadence for stakeholders and define escalation triggers such as exceedance of error thresholds, sudden CSAT drops or identified safety issues that require immediate rollback.
Decision criteria, integrations and common vendor questions
When to build vs. integrate a hosted ChatGPT-style API
Choose build when you need maximum control over data, custom model behaviour or internal hosting to meet strict compliance needs. Choose integrate when speed to market, lower engineering cost and vendor-managed model operations are priorities.
Consider the sensitivity of the data you will process, the team capacity to operate monitoring and incident response, and how quickly you must deploy new features when making this decision.
Operational integrations with ticketing, CRM and human handoff
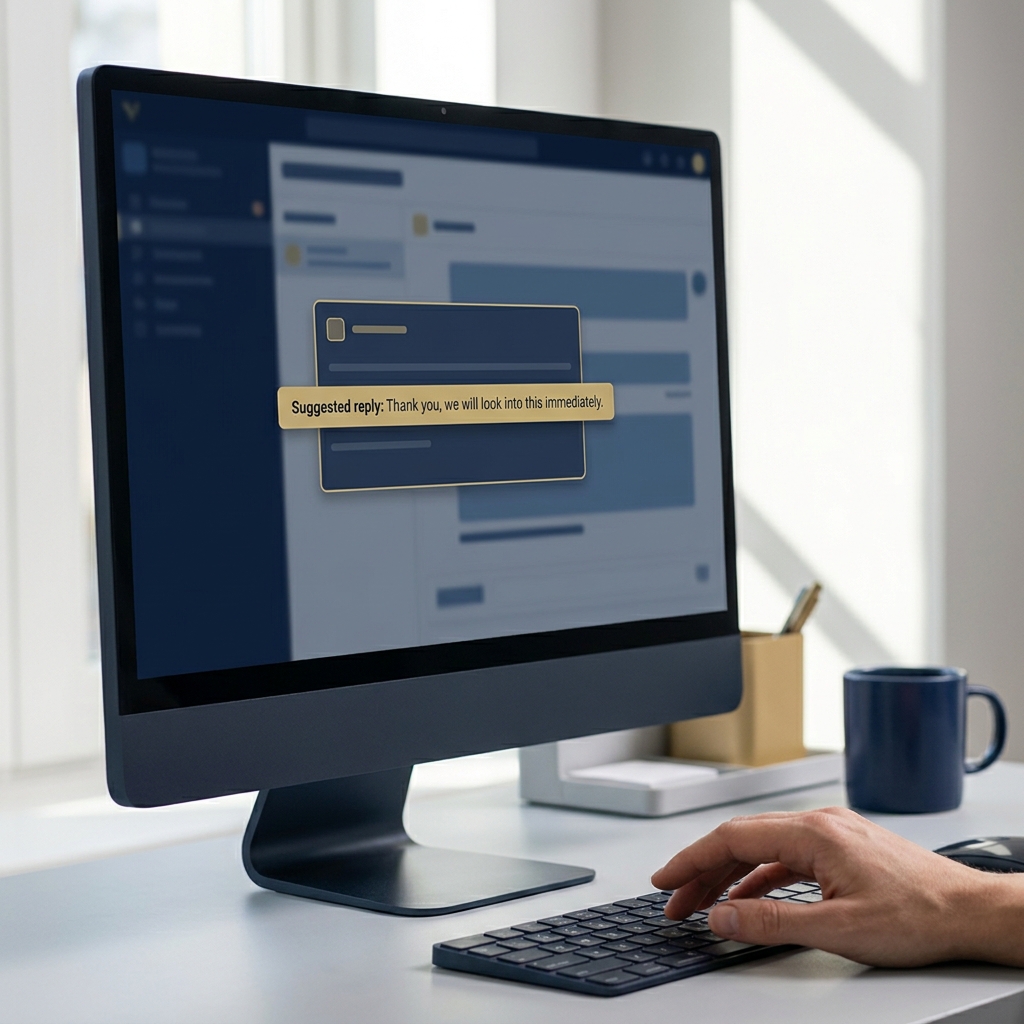
Plan integrations that preserve session continuity and map model outputs to ticket fields in your CRM so agents see context and can pick up conversations without repeating questions. Use agent assist UIs that show confidence signals and suggested replies rather than auto-submitting content into a ticket.
Ensure escalation pathways are seamless, including clear audit trails of when and why a handoff happened and what data accompanied it to the human agent.
Vendor and contract checklist
Confirm data usage and retention terms, model update policies, incident response SLAs, audit rights and liability allocation. Ensure contract language aligns with your deployment model and privacy obligations, and include provisions for security reviews and periodic compliance reports.
When relying on hosted APIs review the provider documentation and contractual guarantees for data handling and implement technical safeguards such as request filtering and logging controls to meet your stated retention limits OpenAI API data usage policies.
Typical pitfalls, troubleshooting and a short operational checklist to close
Common mistakes that erode trust or compliance
Teams commonly skip a DPIA, under-invest in human oversight, or rely on vendor defaults for sensitive data handling. These missteps lead to regulatory risk and loss of customer trust.
Poor metric tracking or ambiguous escalation rules also erode outcomes because teams cannot reliably identify drift or safety regressions.
How to triage performance and safety incidents
For hallucinations or unsafe outputs, isolate the conversation, capture logs, and follow the incident playbook to remove harmful content, update prompts and notify affected users where required. Escalate legal or regulatory concerns to counsel and security incidents to your security operations team.
For data leak or retention concerns, freeze ingestion, audit recent requests, and verify whether vendor logs or backups contained the exposed data, then act according to your breach response plan and local notification rules.
One-page pre-launch checklist
Complete a rapid pre-launch checklist that covers governance, DPIA, prompt standards, access controls, monitoring, escalation pathways, agent training, staged rollout and documented vendor terms.
Keep the checklist accessible to engineers, product and legal teams, and run a tabletop incident drill before the first public release to validate handoffs and communications.
Frequently asked questions
Do I need to tell users they are talking to an AI?
Yes, transparency requirements in many jurisdictions require informing users when they interact with AI; follow local rules and document disclosures.
Will using a ChatGPT API automatically train the provider's models?
Provider policies may vary; some public documentation states API inputs and outputs are not used to train models by default, but verify contract terms and configuration.
What metrics show an AI chatbot is working?
Track containment, first-contact resolution, CSAT, average handle time, escalation rate and safety or accuracy error rates to evaluate performance.
If you are evaluating a production deployment, use the lifecycle and checklist here to map responsibilities and timelines. Consult legal and security specialists for jurisdictional requirements and contract reviews before going live. A staged pilot with clear metrics and escalation rules will show whether automation delivers the expected quality and cost benefits while keeping customers safe.